

OP 29 August, 2026 - 09:18 PM
According to the US Department of Justice, the group known as QTFY/QT/QTCYBER used two "hacking platforms"—QScan and QTRouter—to attack US critical infrastructure and other secure networks .

LIFETIME
QTFY's targets included NASA, the US Federal Reserve, the Departments of Energy, Justice, Health and Human Services, the National Institutes of Health, and the US Senate.
The US Department of Justice reports that the QTFY group created and operated the QScan and QTRouter platforms and works for the China-based Nanjing Xinjiuwei Network Technology Company.
Court documents indicate that the group includes former members of the People's Liberation Army, and that Nanjing Xinjiuwei received payments from China's Ministry of State Security (MSS). This indicates that "the company is conducting malicious cyber activities on behalf of the Chinese government."
The affidavit supporting the lawsuit states that QTFY used the domains qtproxy[.]xyz , qt-proxy[.]org , and qt-team[.]com to operate QScan, described as a "scanning and exploitation platform," and QTRouter, described as a "traffic obfuscation network."
All three domains were seized by authorities and now display law enforcement notices.
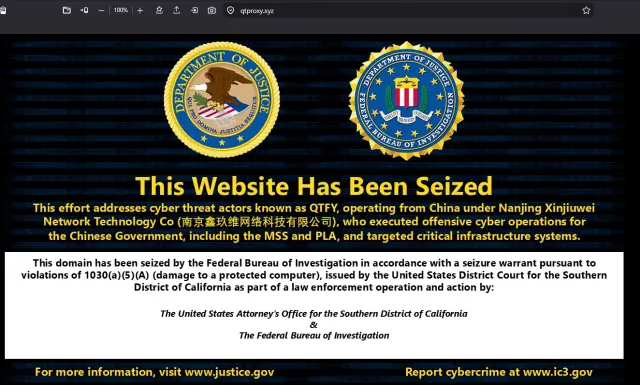
The QTFY domain seized by the FBI.
Source: BleepingComputer.
Black Lotus Labs, the research division of Lumen Technologies, has been monitoring QTFY's infrastructure for the past year and discovered platform components used in attacks on US critical infrastructure.
According to researchers, the provider offers a reusable service consisting of four distinct operational components:
Researchers also note that they disrupted the infrastructure by null-routing traffic to known infrastructure points used by quartermaster operators.
According to Lumen, "quartermaster" industrialized the creation of Operational Relay Box (ORB) networks for operators of China-linked espionage campaigns.
ORBs are decentralized networks of compromised infrastructure, including SOHO routers, IoT devices, VPS servers, and commercial proxy nodes. They are used to relay malicious traffic and obscure its true source.
QTFY also sold access to QScan and QTRouter to other attackers, allowing them to scan vulnerable IoT devices and exploit them. The hacker group was able to add such devices to the botnet as nodes, obscuring the origin of malicious traffic by routing it through devices belonging to legitimate users.
Since 2024, Chinese hacker groups have increasingly used ORB networks in their cyber operations, and they further intensified such activity earlier this year.
In the case of "Quartermaster," instead of creating a traditional ORB network of thousands of compromised devices, the platform acquired premium access to select nodes operated by the Chinese commercial proxy service fastlink.ws .
These nodes formed Fast Labyrinth—an ORB-like relay network that mixed spy traffic with regular user traffic from the commercial proxy service and automatically changed the internet access infrastructure.
Researchers consider the coincidence between QScan's targets and the organizations subsequently connected to via Fast Labyrinth to be the most compelling evidence of a link between intelligence activities and subsequent operations.
Lumen believes that the observed bidirectional connections from the proxy network likely indicate attempts to exploit vulnerabilities, lateral movement within the network, gain access, or collect data.
While the disruption of this provider is significant, Lumen warns that a static block alone will likely not be sufficient. This is because quartermaster's traffic is routed through dynamically changing commercial proxy services.
The US Department of Justice reports that the QTFY group created and operated the QScan and QTRouter platforms and works for the China-based Nanjing Xinjiuwei Network Technology Company.
Court documents indicate that the group includes former members of the People's Liberation Army, and that Nanjing Xinjiuwei received payments from China's Ministry of State Security (MSS). This indicates that "the company is conducting malicious cyber activities on behalf of the Chinese government."
The affidavit supporting the lawsuit states that QTFY used the domains qtproxy[.]xyz , qt-proxy[.]org , and qt-team[.]com to operate QScan, described as a "scanning and exploitation platform," and QTRouter, described as a "traffic obfuscation network."
All three domains were seized by authorities and now display law enforcement notices.
The QTFY domain seized by the FBI.
Source: BleepingComputer.
Black Lotus Labs, the research division of Lumen Technologies, has been monitoring QTFY's infrastructure for the past year and discovered platform components used in attacks on US critical infrastructure.
According to researchers, the provider offers a reusable service consisting of four distinct operational components:
- QScan is a reconnaissance component that identifies and profiles high-value targets by collecting information about open ports, application banners, operating system characteristics, and system configuration.
- Fast Labyrinth is an encrypted relay network that obscures communications between attackers and victim organizations.
- QTRouter is a pre-configured physical device that provides access to the proxy infrastructure and node management system.
- QTProxy is a management tool that allows users to select repeaters and configure their own routes through Fast Labyrinth.
Quote:"Lumen Technologies would like to thank the FBI and the Department of Justice for their efforts to counter Chinese cyber activity targeting U.S. critical infrastructure," the report said.
Quote:"During our investigation, Black Lotus Labs shared threat intelligence to alert U.S. government agencies to emerging risks that could impact our nation's strategic assets."
Researchers also note that they disrupted the infrastructure by null-routing traffic to known infrastructure points used by quartermaster operators.
According to Lumen, "quartermaster" industrialized the creation of Operational Relay Box (ORB) networks for operators of China-linked espionage campaigns.
ORBs are decentralized networks of compromised infrastructure, including SOHO routers, IoT devices, VPS servers, and commercial proxy nodes. They are used to relay malicious traffic and obscure its true source.
QTFY also sold access to QScan and QTRouter to other attackers, allowing them to scan vulnerable IoT devices and exploit them. The hacker group was able to add such devices to the botnet as nodes, obscuring the origin of malicious traffic by routing it through devices belonging to legitimate users.
Since 2024, Chinese hacker groups have increasingly used ORB networks in their cyber operations, and they further intensified such activity earlier this year.
In the case of "Quartermaster," instead of creating a traditional ORB network of thousands of compromised devices, the platform acquired premium access to select nodes operated by the Chinese commercial proxy service fastlink.ws .
These nodes formed Fast Labyrinth—an ORB-like relay network that mixed spy traffic with regular user traffic from the commercial proxy service and automatically changed the internet access infrastructure.
Researchers consider the coincidence between QScan's targets and the organizations subsequently connected to via Fast Labyrinth to be the most compelling evidence of a link between intelligence activities and subsequent operations.
Lumen believes that the observed bidirectional connections from the proxy network likely indicate attempts to exploit vulnerabilities, lateral movement within the network, gain access, or collect data.
While the disruption of this provider is significant, Lumen warns that a static block alone will likely not be sufficient. This is because quartermaster's traffic is routed through dynamically changing commercial proxy services.
LIFETIME